
Nuclei Online Vulnerability Scan
Template-based scanner for CVEs, exposed files, misconfigurations, and default credentials across web apps, APIs, and infrastructure
10,000+
signed templates in the official nuclei-templates project
1,400+
templates for vulnerabilities on the CISA and VulnCheck KEV lists
31,000+
GitHub stars
Nuclei template scanning on HostedScan
Nuclei runs thousands of community-written templates against your targets and reports exact matches. HostedScan hosts the scanner and runs only signed templates, so you get the coverage without maintaining a scanner.
10,000+ signed templates
The official nuclei-templates project, signed templates only
3,500+ CVE templates
Including 1,400+ templates for vulnerabilities on the CISA and VulnCheck KEV lists
Exposures and misconfigurations
Exposed .git and .env files, public Swagger docs, missing security headers, CORS
Default credentials
Grafana, Jenkins, and other admin panels still on factory logins
Web, API, and network
HTTP, DNS, SSL, and network templates in one run
Rate limited
Request rates are capped per scan to keep load on production low
Template-based scanning for known vulnerabilities
Nuclei is an open-source scanner from ProjectDiscovery. Instead of fingerprinting software versions, it runs YAML templates that each describe one check: the requests to send and the response that confirms the issue. The nuclei-templates project maintains more than 10,000 templates, and new ones land within hours of a major disclosure.
HostedScan runs Nuclei against websites, APIs, and hosts, then reports every match as a risk with the template name, severity, and the URL it matched at. Because Nuclei looks for direct evidence of a vulnerability, it pairs well with OpenVAS, which infers vulnerabilities from versions and configurations. Running both catches issues that either one alone would miss.
How HostedScan runs Nuclei
A template describes the exploit:
Each template sends the requests needed to trigger a specific issue and matches on the response. A finding means the target responded the way the vulnerable software does, which keeps false positives low.
Signed templates only:
HostedScan runs the official nuclei-templates project and skips unsigned templates, templates that need a headless browser, and templates that need an out-of-band callback server.
Tuned for production targets:
Every scan runs under a request rate cap, and redirects are followed on the same host only. Scans stay light on the target and never follow redirects to third-party domains.
HostedScan runs 10,000+ signed templates from the official nuclei-templates project.
Template ids, names, and severities as they appear in the project and in HostedScan results.
Ready to run a Nuclei scan in seconds?
Get the full power of Nuclei without installing a thing. That's HostedScan.
Six scanners, one dashboard
Nuclei plus five more scanners
Point more than one scanner at a target and work every finding from the same risk list.
Benefits of using HostedScan
What HostedScan adds to Nuclei
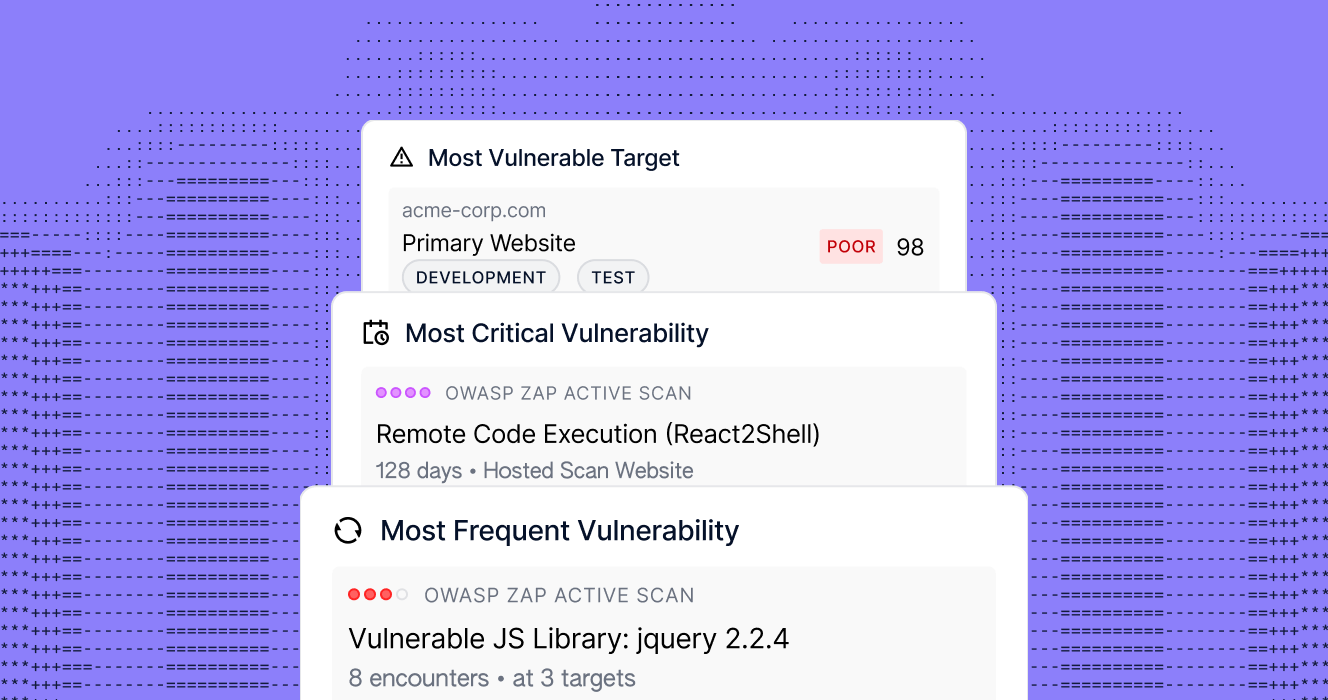
Mitigate security vulnerabilities
Discover CVEs, OWASP Top 10 vulnerabilities, and exploitable weaknesses across your entire infrastructure. Get prioritized remediation guidance with CVSS scoring and actionable risk classifications. Fix what matters first.
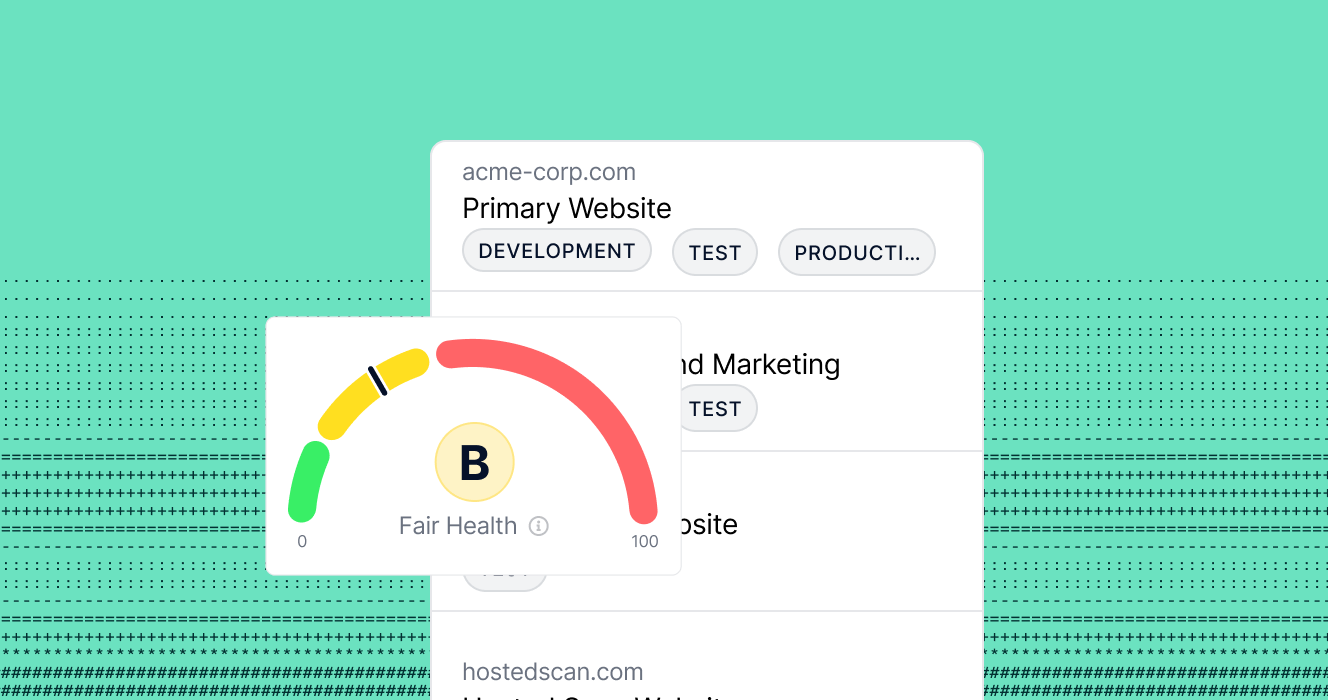
Manage your risk exposure
With regulations such as GDPR and CCPA, failure to maintain reasonable security procedures is grounds for lawsuits and fines.
Meet compliance requirements
Vulnerability scanning is essential for your compliance with SOC 2, ISO 27001, cyber insurance, and more.
Detect misconfigurations
90% of cyber attacks exploit simple misconfigurations, not zero-days. Detect exposed ports, weak credentials, outdated software, and common security gaps before attackers do: automatically, every day.
Map your attack surface
Your infrastructure changes constantly. Automatically discover and monitor all websites, servers, networks, and APIs, maintaining complete visibility of your attack surface without manual tracking.
14 days free. No credit card required.
See a sample reportOur Customers
5,000+ MSPs and IT teams who move faster


Quick Answers
Frequently asked questions
Our knowledge base contains answers to technical questions, and you can always contact us for more details on our plans, pricing, or any questions.
Speed and power,
without the complexity
The world's leading vulnerability scanners, all in one platform.