
SSLyze Online Scan
TLS and SSL vulnerability scanner for certificates, protocol versions, and known attacks
SSL 2.0 to TLS 1.3
every protocol version and cipher suite enumerated
1 to 5 min
per host, from connection to report
TLS configuration scanning with SSLyze
SSLyze reports exactly what a TLS configuration exposes. HostedScan wraps it in a managed platform with continuous monitoring, alerts, and a risk dashboard that tracks each issue over time.
Heartbleed, ROBOT, CCS
Tests for the known OpenSSL and RSA padding oracle attacks
TLS 1.0 and 1.1
Flags deprecated protocol versions that are still enabled
Certificate validation
Expired, self-signed, and untrusted certificates, and chains served out of order
Renegotiation
Client renegotiation denial of service and insecure renegotiation
1 to 5 minutes
Per host, so it fits any schedule
A fast, thorough TLS configuration scanner
SSLyze is an open-source TLS scanner. It connects to a server, enumerates every protocol version from SSL 2.0 to TLS 1.3 and the cipher suites accepted for each, validates the certificate chain against the major trust stores, and tests for known attacks such as Heartbleed, the OpenSSL CCS injection, and ROBOT.
HostedScan runs SSLyze against any hostname or IP address and turns the results into risks with a severity and a fix. A scan takes one to five minutes per host, which makes it the right scan to schedule daily on every certificate you own.
Getting a clean SSLyze result
Disable TLS 1.0 and 1.1:
PCI DSS required TLS 1.0 to be retired in 2018, and TLS 1.1 is deprecated by RFC 8996. Serve TLS 1.2 and TLS 1.3 only, and confirm the change with a rescan.
Serve the full certificate chain in order:
Browsers can sometimes recover from a missing or misordered intermediate certificate, but API clients and older devices often cannot. SSLyze validates the chain the way a strict client does.
Scan every hostname daily:
A scan takes one to five minutes, so run it on a daily schedule against every hostname with a certificate. An expired certificate or a configuration change shows up as a new finding the same day.
Every finding is a configuration you can fix.
Each finding includes a description of the attack or misconfiguration and how to fix it.
Ready to run an SSLyze scan in seconds?
Get the full power of SSLyze without installing a thing. That's HostedScan.
Six scanners, one dashboard
SSLyze plus five more scanners
Point more than one scanner at a target and work every finding from the same risk list.
Benefits of using HostedScan
What HostedScan adds to SSLyze
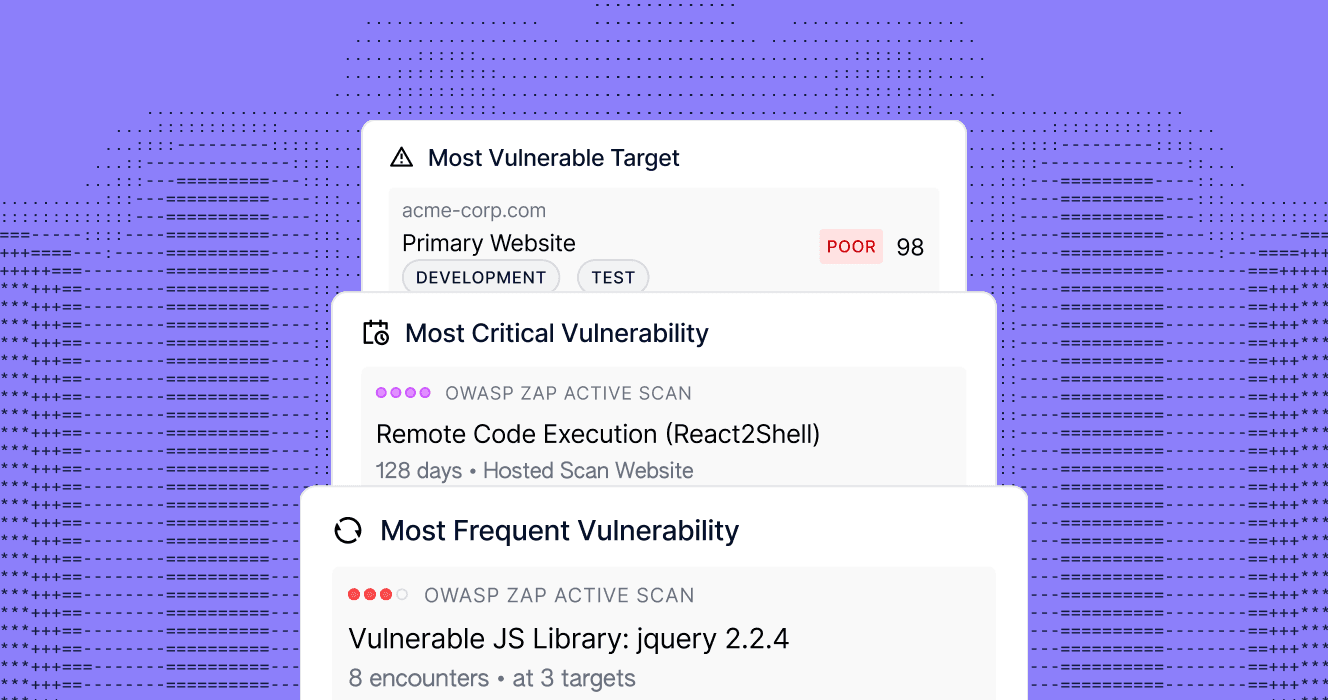
Mitigate security vulnerabilities
Discover CVEs, OWASP Top 10 vulnerabilities, and exploitable weaknesses across your entire infrastructure. Get prioritized remediation guidance with CVSS scoring and actionable risk classifications. Fix what matters first.
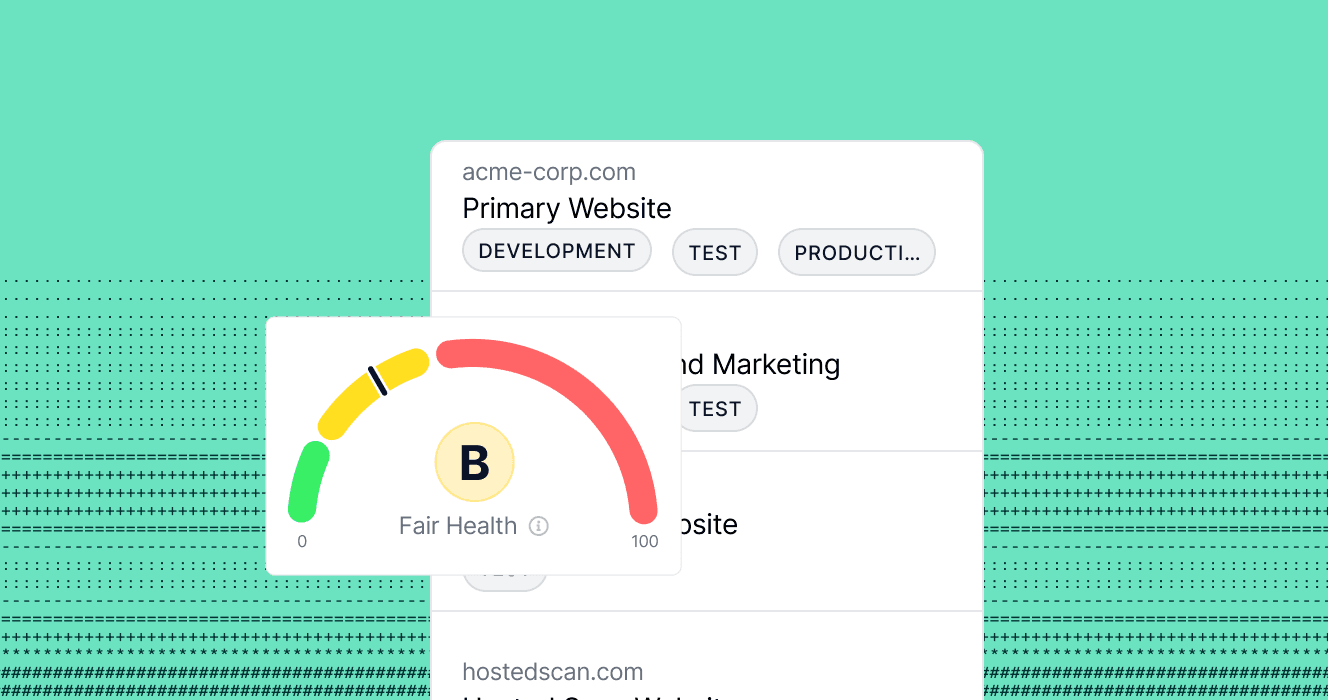
Manage your risk exposure
With regulations such as GDPR and CCPA, failure to maintain reasonable security procedures is grounds for lawsuits and fines.
Meet compliance requirements
Vulnerability scanning is essential for your compliance with SOC 2, ISO 27001, cyber insurance, and more.
Detect misconfigurations
90% of cyber attacks exploit simple misconfigurations, not zero-days. Detect exposed ports, weak credentials, outdated software, and common security gaps before attackers do: automatically, every day.
Map your attack surface
Your infrastructure changes constantly. Automatically discover and monitor all websites, servers, networks, and APIs, maintaining complete visibility of your attack surface without manual tracking.
14 days free. No credit card required.
See a sample reportOur Customers
5,000+ MSPs and IT teams who move faster


Quick Answers
Frequently asked questions
Our knowledge base contains answers to technical questions, and you can always contact us for more details on our plans, pricing, or any questions.
Speed and power,
without the complexity
The world's leading vulnerability scanners, all in one platform.