
OWASP ZAP Online Scan
Website and web application vulnerability scanner
#1
most widely used web application security scanner
15,000+
GitHub stars
15+ years
as the industry standard for DAST
OWASP ZAP scanning on HostedScan
HostedScan runs OWASP ZAP for you through an online dashboard, always up to date, with a risk management platform to reduce noise and stay compliant with SOC 2, ISO 27001, and more.
OWASP Top 10
Detect XSS, SQL injection, and other OWASP Top 10 risks
Passive and active
A safe passive crawl in minutes, or a full active scan that submits forms and payloads
SPA support
Crawls traditional HTML sites and React, Angular, or Vue single-page apps
JS library scanning
Discover vulnerable JavaScript libraries in your apps
API scanning
Scan APIs more thoroughly with an OpenAPI definition
Authenticated scans
Scan behind logins with a recorded login, a session cookie, or a header
OWASP security scan details
HostedScan provides two OWASP security scans. Both use the OWASP ZAP (Zaproxy) scanner, an open source project.
These scans test websites and web apps for OWASP Top 10 risks. ZAP is an open-source dynamic application security testing tool covering SQL injection, XSS, and dozens of other vulnerability classes.
The Passive Scan
Loads the pages of a website and checks for vulnerabilities such as cross-domain misconfigurations, insecure cookies, and vulnerable JS dependencies.
Fast: Completes within several minutes
Safe: Non-intrusive scanning method
Complete: Checks configuration and informational issues
The Active Scan
Submits forms and makes requests to the web application to test for vulnerabilities such as SQL injection, remote command execution, and cross-site scripting.
Extensive: Thorough testing of all vulnerabilities
Permission Required: Make sure you have authorization
Thorough: May take several hours for complete coverage
OWASP ZAP detects hundreds of vulnerabilities.
Every test runs in the active scan. The passive column shows which tests also run without submitting forms or sending payloads.
Ready to run a ZAP scan in seconds?
Get the full power of OWASP ZAP without installing a thing. That's HostedScan.
Six scanners, one dashboard
OWASP ZAP plus five more scanners
Point more than one scanner at a target and work every finding from the same risk list.
Benefits of using HostedScan
What HostedScan adds to OWASP ZAP
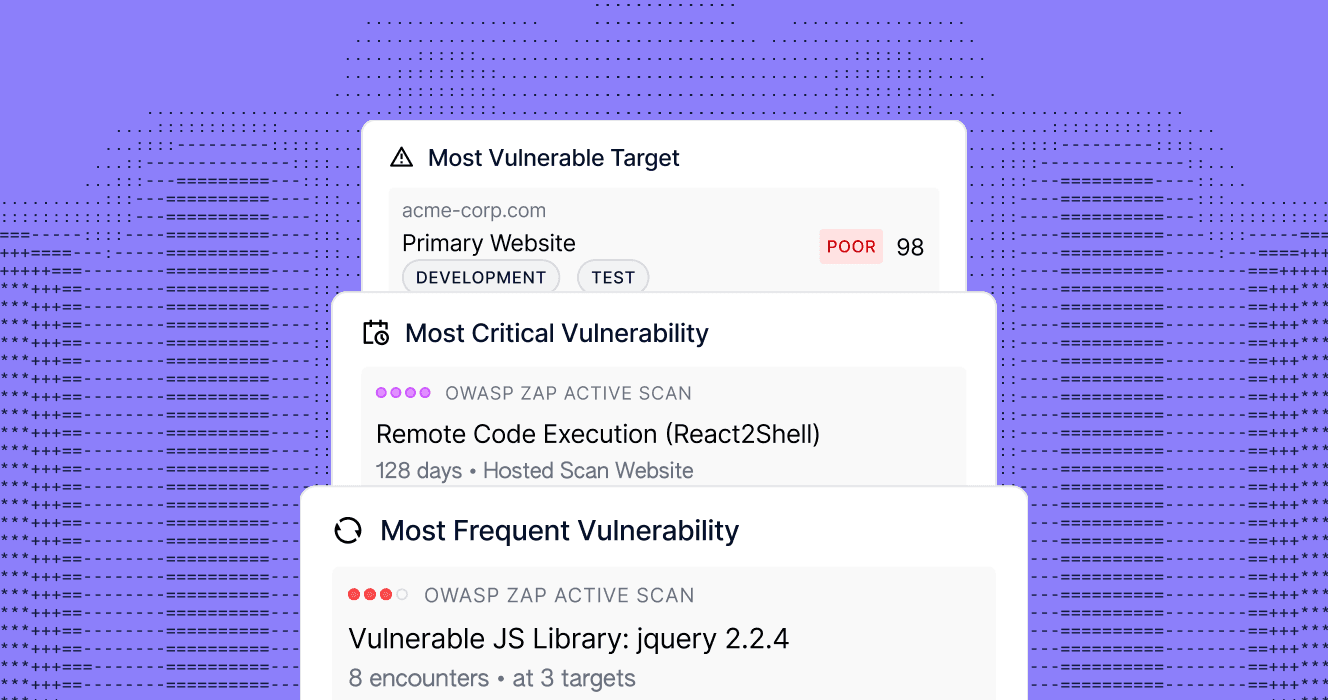
Mitigate security vulnerabilities
Discover CVEs, OWASP Top 10 vulnerabilities, and exploitable weaknesses across your entire infrastructure. Get prioritized remediation guidance with CVSS scoring and actionable risk classifications. Fix what matters first.
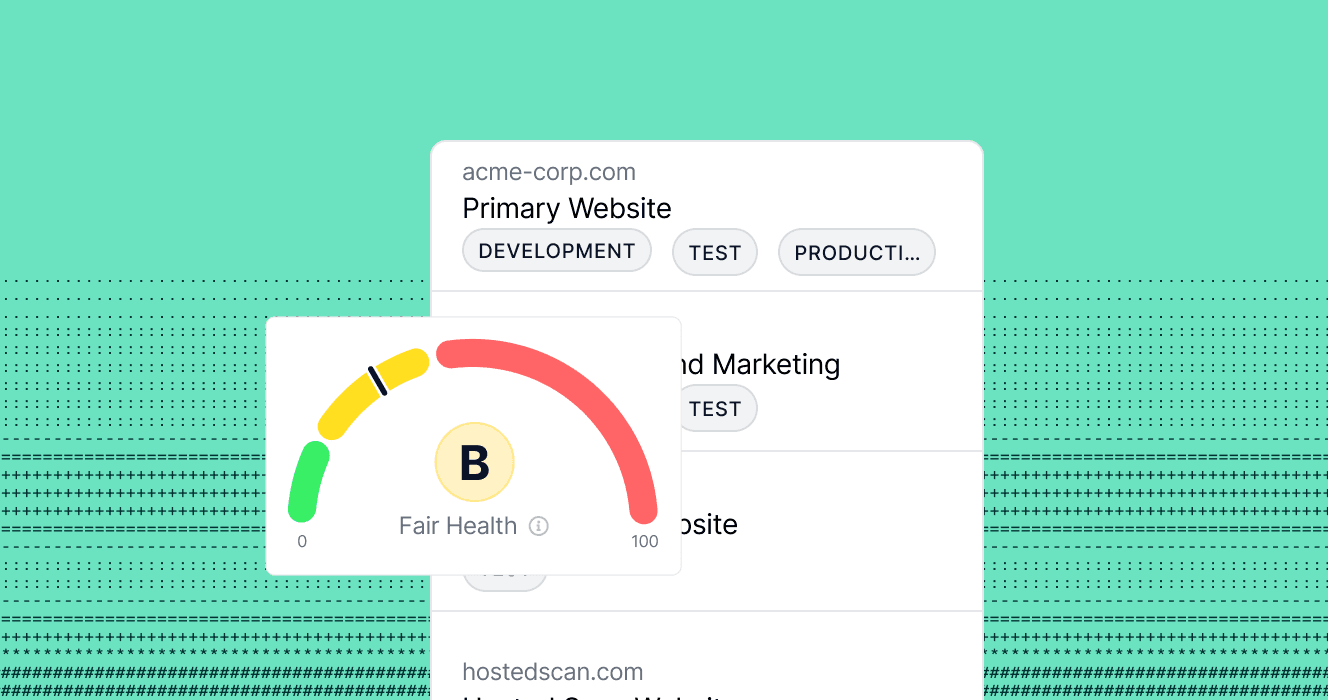
Manage your risk exposure
With regulations such as GDPR and CCPA, failure to maintain reasonable security procedures is grounds for lawsuits and fines.
Meet compliance requirements
Vulnerability scanning is essential for your compliance with SOC 2, ISO 27001, cyber insurance, and more.
Detect misconfigurations
90% of cyber attacks exploit simple misconfigurations, not zero-days. Detect exposed ports, weak credentials, outdated software, and common security gaps before attackers do: automatically, every day.
Map your attack surface
Your infrastructure changes constantly. Automatically discover and monitor all websites, servers, networks, and APIs, maintaining complete visibility of your attack surface without manual tracking.
14 days free. No credit card required.
See a sample reportOur Customers
5,000+ MSPs and IT teams who move faster


Quick Answers
Frequently asked questions
Our knowledge base contains answers to technical questions, and you can always contact us for more details on our plans, pricing, or any questions.
Speed and power,
without the complexity
The world's leading vulnerability scanners, all in one platform.