Comparison
Invicti vs. HostedScan
Invicti, formerly Netsparker, is an enterprise application security platform with proof-based DAST. HostedScan covers web apps and APIs with OWASP ZAP and adds network, TLS, port, and Nessus scanning.
Try the Premium plan free for 14 days. No credit card required.

At a glance
HostedScan
Invicti
Starting price
$468 / year, 5 targets
Quote
Scanners
OpenVAS, Nuclei, ZAP, Nmap, SSLyze; Nessus on Professional
Proof-based DAST
Internal scanning
Included from Premium
Web apps only, via agent
Trial
14 days, no card
Proof of concept through sales
Differences
What sets HostedScan apart from Invicti
Beyond the application layer
Invicti scans web apps and APIs. HostedScan scans those plus servers, networks, TLS, and ports, with Tenable Nessus on Professional.
A price on the page
HostedScan Premium is $109 per month billed annually for five targets. Invicti plans are quoted and sized for enterprise portfolios.
Scanning in minutes
Sign up and run a ZAP scan today. Invicti evaluations run through a demo and a proof-of-concept license.
Open-source scanners you can inspect
Every check comes from OWASP ZAP, Greenbone OpenVAS, Nuclei, Nmap, or SSLyze, and each finding names its scanner.
Inside the product
What you get on day one
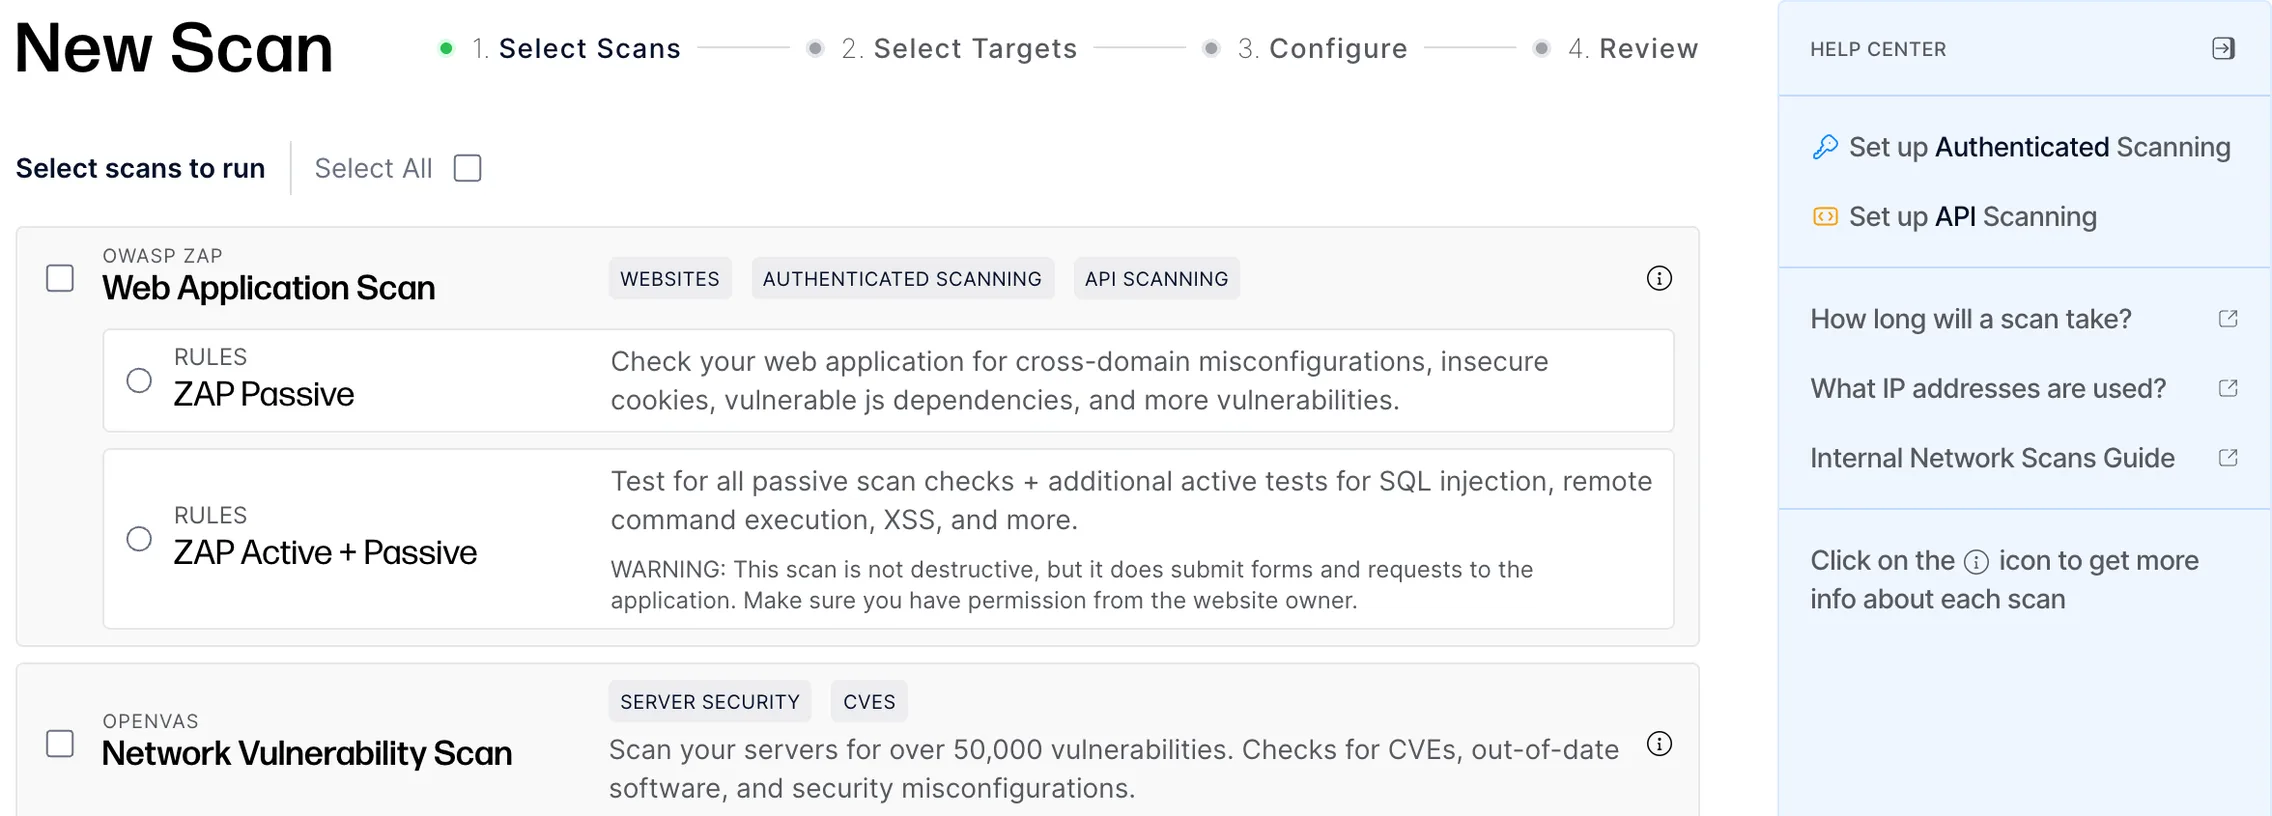
One scan can run ZAP against the app and OpenVAS, Nuclei, Nmap, and SSLyze against the hosts behind it, with every finding in the same triage workflow.
Which one fits
Choose HostedScan if
- You need servers and networks scanned alongside the apps, in one list.
- You have a few apps and a budget closer to $1,308 per year billed annually than to an enterprise contract.
- You want to start today, without a proof-of-concept license.
- You want SOC 2 and ISO 27001 evidence across infrastructure as well as apps.
Choose Invicti if
- You run a large app portfolio and need proof-based scanning to cut triage.
- You want SCA, SBOMs, and CI/CD gating in the same platform.
- You require on-premises or air-gapped deployment.
- You have an AppSec team to tune scan policies per app.
Capability matrix
Feature by feature
Differences come first. A half circle marks a limited capability, and its note names the limit. Notes about Invicti link to their source.
Feature


Scanners
Proof-based exploit confirmation
No exploitation tools. Findings ship with evidence and remediation steps.
Safely exploits many findings to prove they are real.
SourceNetwork CVE scanning
Greenbone OpenVAS and Nuclei CVE scanning plus Nmap TCP and UDP port scans on every plan, and Tenable Nessus on Professional.
Application security platform; no network vulnerability scanner.
SourceDedicated TLS and port scanners
SSLyze certificate, protocol, and cipher checks on every plan.
TLS findings only as they relate to the web application.
SourceTenable Nessus
Nessus cloud scanning, Nessus scanners for internal networks, and Nessus Agents, all on Professional.
No third-party network scanner.
SourceSoftware composition analysis
No software composition analysis. Dependabot and Snyk results can be imported into the same risk list.
SCA and SBOM generation included.
SourceCoverage
Internal network scanning
An internal scanner runs inside your network on Premium. Nessus scanners and Nessus Agents on Professional.
SourceInternal agents scan internal web apps only.
SourceOn-premises deployment
Cloud platform only. The internal scanner runs on your network; the dashboard does not.
On-premises and air-gapped on AppSec Flex; other plans are cloud. Web + API lists on-premises as coming soon.
SourceReporting and risk management
Health score over time
A health score per target and per account, trended over time.
Trend dashboards; no per-target grade.
SourceWhite-label reports
White-label PDF reports with your branding on Professional.
Custom report templates with your logo.
SourceImport results from other scanners
Connect GitHub Dependabot and Snyk, and upload Nmap, OpenVAS, or ZAP results through the API.
SourceInvicti ASPM fetches findings from other security tools.
SourceIntegrations and API
Licensing, pricing, and support
Published price list
Published plans from $39 per month billed annually. Per-target rates on the pricing page.
Web + API, AppSec Core, and AppSec Flex are quote-based.
SourceStart without a sales call
Sign up, add a target, scan. Sales is optional at any size.
Demo and proof-of-concept license through sales.
SourceTrial without a card
14-day Premium trial, no credit card.
Proof-of-concept licenses are arranged by request.
SourceHow the two products run
External scanning
Hosted scanners. Add a URL and scan.
Cloud platform, or on-premises on AppSec Flex.
Internal scanning
The internal scanner on Premium reaches internal apps and hosts.
Internal scan agents for applications behind the firewall.
Scanner upkeep
HostedScan maintains the scanners and syncs the Greenbone feed daily.
Invicti maintains the scanner; on-premises customers apply updates.
Where data lives
HostedScan cloud with export and API.
Invicti cloud, your cloud, or on-premises depending on plan.
What your team does weekly
Triage one list across apps and infrastructure.
Tune scan policies, triage confirmed findings, gate builds.
Pricing example
5 web applications with authenticated and API scanning, plus their servers
One scenario priced on both products. HostedScan totals come from the published plan and per-target rates. Invicti figures were checked in September 2026 and link to the source.
HostedScan Premium
$1,308 / year
$109 per month billed annually. 5 targets included.
Premium includes authenticated ZAP scans, OpenAPI scanning, OpenVAS and Nuclei for the servers, Nmap, SSLyze, and the API.
Invicti
Quote
Web + API, AppSec Core, and AppSec Flex plans are quoted per application portfolio. Invicti publishes one price: Agentic Pentest at up to $500 per pentest.
From our customers
What our customers say
“HostedScan is our trusted partner for OWASP Top 10 testing and proactive security. Their platform is powerful, but it’s their dedicated support team that truly sets them apart.”
Victor Beitner • Founder

“I found your platform to be best-in-class for automated vulnerability assessment and reporting. I've already started suggesting it to other software teams.”
Orane Cole • Founder & CEO

“As a SaaS company we are constantly at risk of cyberattacks, therefore an effective vulnerability scanner is a critical component of our information security toolkit. After an extensive search for an alternative solution, we found HostedScan and decided to give it a try. We are glad we did.”
Paolo Losi • CEO at Enuan
Quick Answers
Frequently asked questions
Our knowledge base contains answers to technical questions, and you can always contact us for more details on our plans, pricing, or any questions.
Speed and power,
without the complexity
The world's leading vulnerability scanners, all in one platform.