
OpenVAS Online Scan
Online network vulnerability scanner with tens of thousands of vulnerability tests for servers, devices, and networks
Daily
Greenbone Community Feed updates, synced to the scanners as new vulnerabilities are disclosed
20+
years as the leading open-source scanner
100
top UDP ports scanned alongside every IANA-registered TCP port
Easily run OpenVAS vulnerability scans
HostedScan runs OpenVAS for you through an online dashboard, with the reporting and management features needed for a vulnerability management program that satisfies SOC 2, ISO 27001, and more.
Tens of thousands of vulnerability tests
The Greenbone Community Feed, synced to the scanners every day
Every IANA TCP port
A full scan covers all IANA-registered TCP ports plus the top 100 UDP ports
Internal networks
Deploy OpenVAS inside your network with one command, including authenticated scans
Adjustable QoD
Set the quality of detection threshold to trade noise for coverage
Scheduled and alerted
Recurring scans with alerts when a new finding appears
The open-source network vulnerability scanner
OpenVAS is an open-source vulnerability scanner that also goes by Greenbone Community Edition and GVM (Greenbone is the lead maintainer).
OpenVAS tests servers and other network-connected devices with tens of thousands of vulnerability tests in the Greenbone Community Feed, synced daily. This can be done over the internet for publicly exposed systems or over private networks. The scanner first conducts a port scan of every IANA-registered TCP port and the top 100 UDP ports to discover what services are open. It then performs additional fingerprinting and testing to check for CVEs, insecure configurations, and vulnerable outdated software versions.
How to get the best scan results with OpenVAS
Update the vulnerability feed:
OpenVAS uses the Greenbone Community Feed as its source of vulnerability data. Ensure the feed is updated in your installation before starting a scan, so that all of the latest vulnerabilities are tested. Or use a managed service, such as HostedScan, which is updated daily.
Choose the right Quality of Detection (QoD):
QoD is a measure of the reliability of vulnerability tests. The default OpenVAS QoD is 70%. However, that may not be right for all systems. Read our guide to setting the right QoD.
Use the Consider Alive setting:
To optimize speed, OpenVAS will first send a ping request to each target and skip targets which do not respond. While this can save considerable time for very large address spaces, when scanning smaller sets of targets it is better to be thorough, as not all targets may respond to ping. Using HostedScan, targets are always considered alive and scanned fully.
OpenVAS runs tens of thousands of vulnerability tests.
From thousands of CVEs in the feed, these are the ones that show up most in real-world scans.
Ready to run an OpenVAS scan in seconds?
Get the full power of OpenVAS without installing a thing. That's HostedScan.
Six scanners, one dashboard
OpenVAS plus five more scanners
Point more than one scanner at a target and work every finding from the same risk list.
Benefits of using HostedScan
What HostedScan adds to OpenVAS
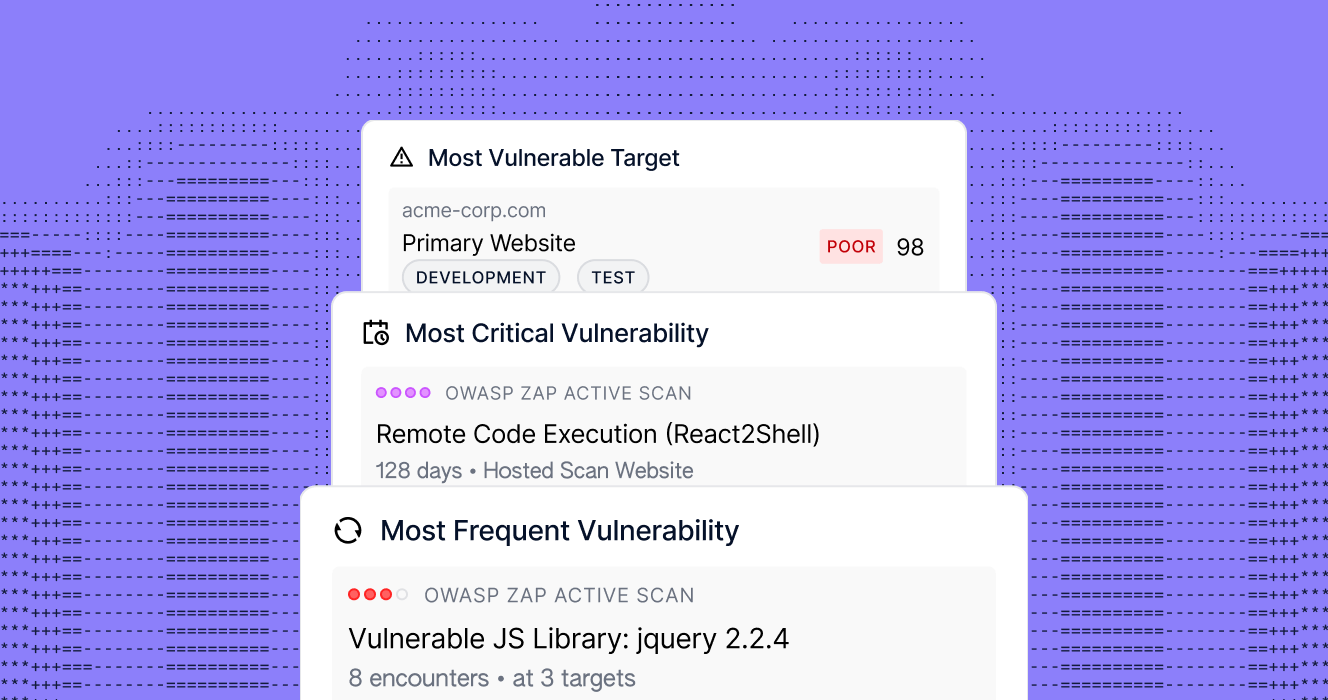
Mitigate security vulnerabilities
Discover CVEs, OWASP Top 10 vulnerabilities, and exploitable weaknesses across your entire infrastructure. Get prioritized remediation guidance with CVSS scoring and actionable risk classifications. Fix what matters first.
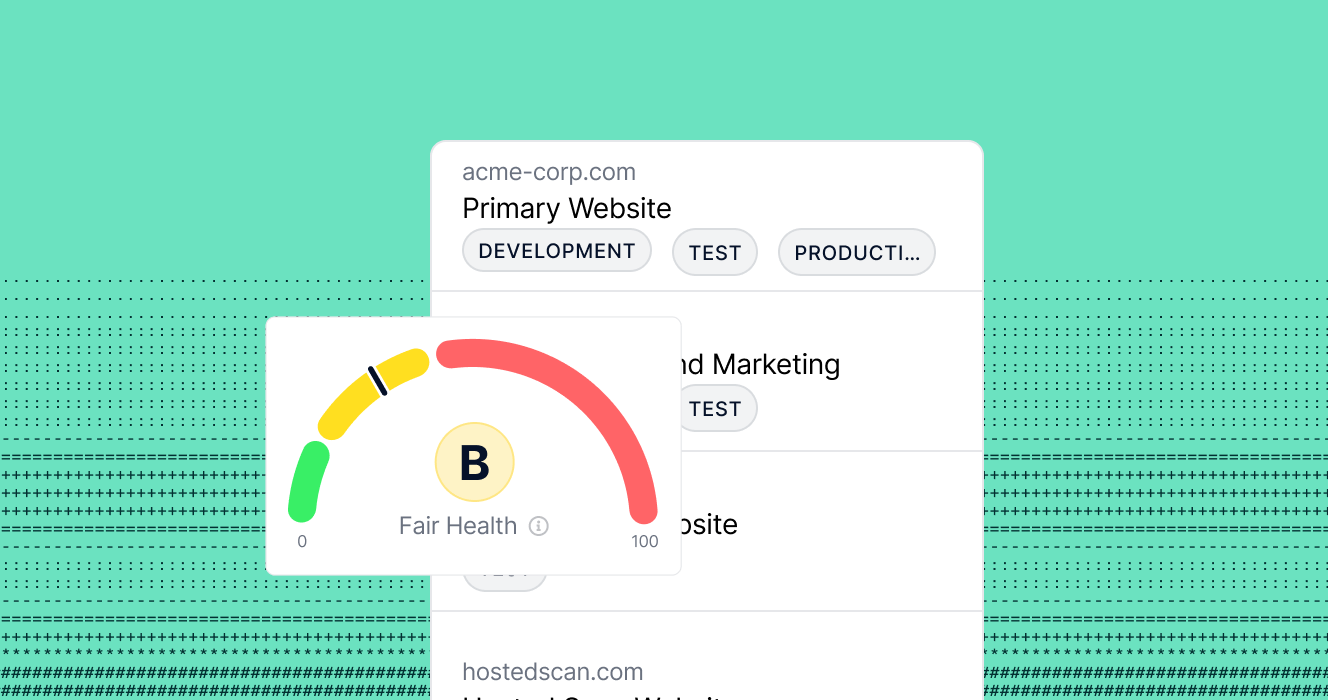
Manage your risk exposure
With regulations such as GDPR and CCPA, failure to maintain reasonable security procedures is grounds for lawsuits and fines.
Meet compliance requirements
Vulnerability scanning is essential for your compliance with SOC 2, ISO 27001, cyber insurance, and more.
Detect misconfigurations
90% of cyber attacks exploit simple misconfigurations, not zero-days. Detect exposed ports, weak credentials, outdated software, and common security gaps before attackers do: automatically, every day.
Map your attack surface
Your infrastructure changes constantly. Automatically discover and monitor all websites, servers, networks, and APIs, maintaining complete visibility of your attack surface without manual tracking.
14 days free. No credit card required.
See a sample reportOur Customers
5,000+ MSPs and IT teams who move faster


Quick Answers
Frequently asked questions
Our knowledge base contains answers to technical questions, and you can always contact us for more details on our plans, pricing, or any questions.
Speed and power,
without the complexity
The world's leading vulnerability scanners, all in one platform.