Comparison
Intruder vs. HostedScan
Intruder and HostedScan run the same scanners: Tenable Nessus, OpenVAS, Nuclei, and ZAP. HostedScan shows which scanner produced each finding, adds Nmap and SSLyze as separate scanners, and imports results from the tools you already run.
Try the Premium plan free for 14 days. No credit card required.

At a glance
HostedScan
Intruder
Starting price
$468 / year, 5 targets
From $299 per month
Scanners
OpenVAS, Nuclei, ZAP, Nmap, SSLyze; Nessus on Professional
OpenVAS, Nuclei, ZAP; Nessus on Pro
Internal scanning
Included from Premium
Pro tier only
Trial
14 days, no card
14 days, free tier
Differences
What sets HostedScan apart from Intruder
Lower price per target
HostedScan plans start at $39 per month billed annually for five targets. Intruder Cloud starts at $299 and Pro at $499 per month for five infrastructure licenses, with web apps priced per app.
Internal scanning from Premium
Intruder ships agent-based internal scanning on Pro. HostedScan includes an internal scanner on Premium and adds Nessus scanners and Nessus Agents on Professional.
Same scanners, every one visible
Both products use Nessus, OpenVAS, Nuclei, and ZAP. HostedScan shows which scanner produced each finding, and adds Nmap and SSLyze as separate scanners.
Bring your own results
Import findings from scanners you already run, plus Dependabot and Snyk, into one risk list. Intruder has no published import for third-party results.
Inside the product
What you get on day one
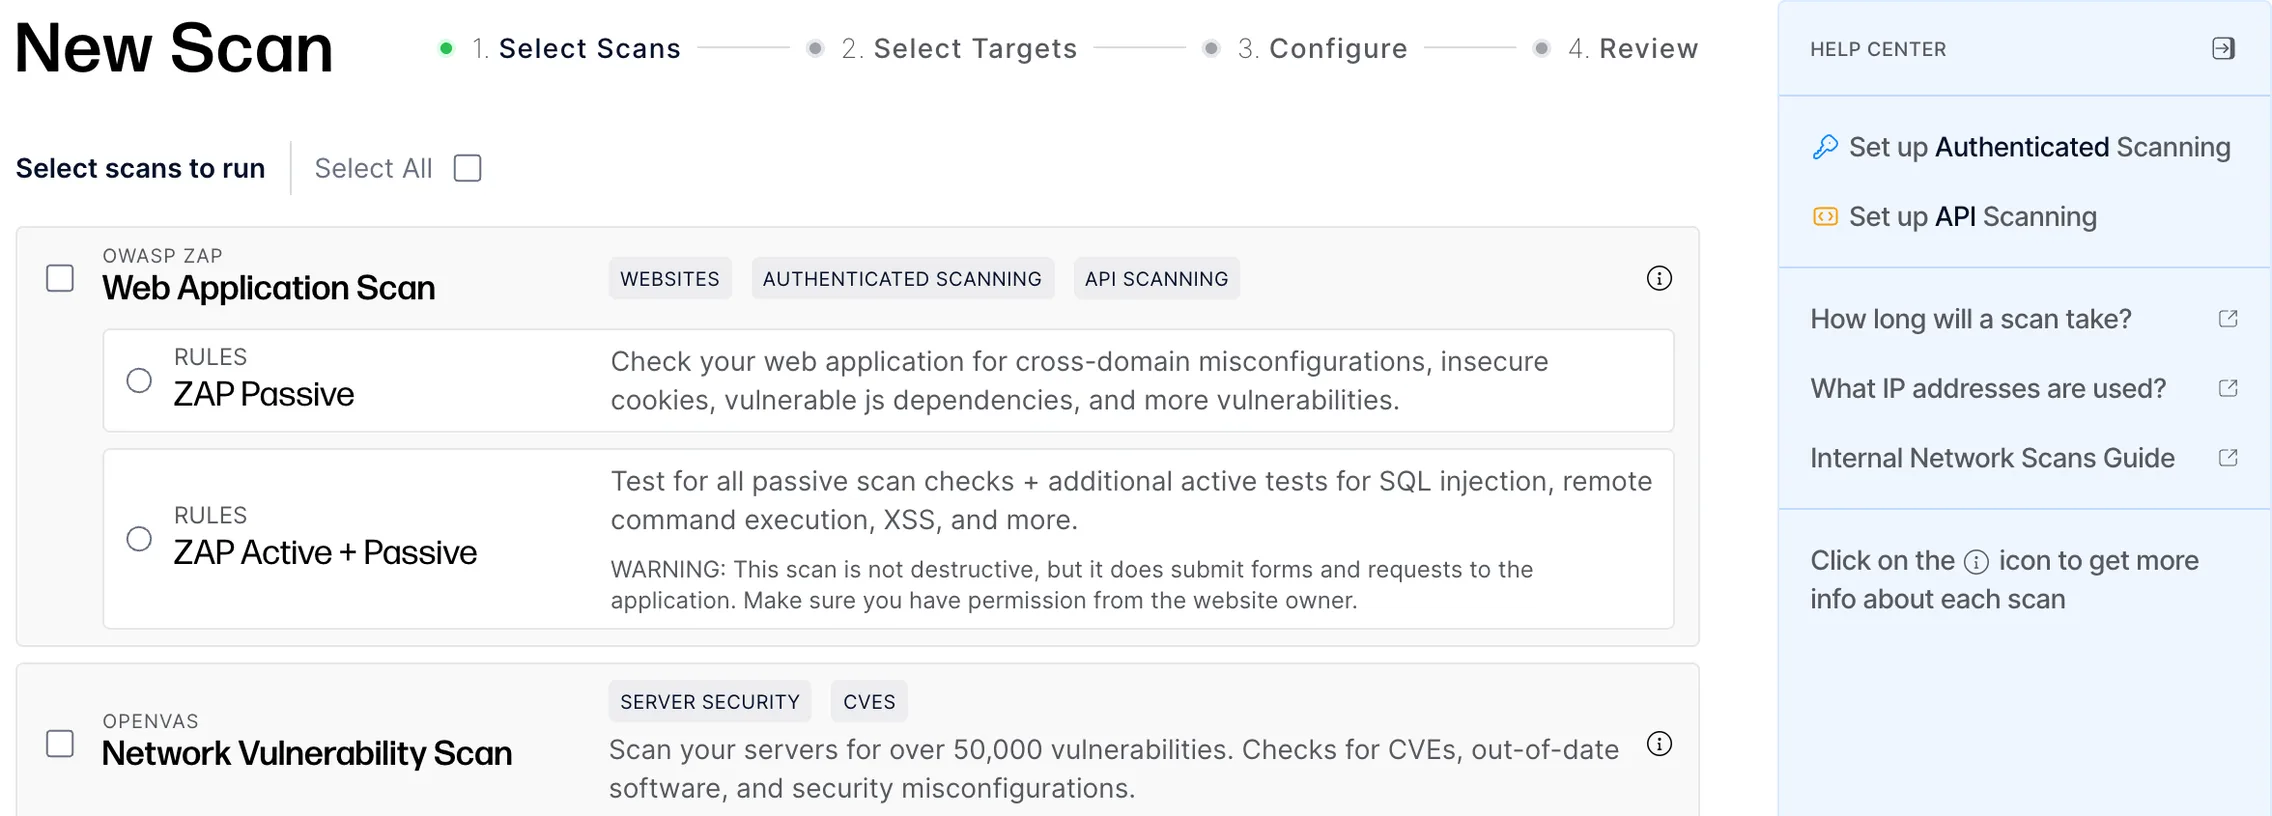
Pick the scanners per scan: ZAP, OpenVAS, Nuclei, Nmap, and SSLyze, with Nessus on Professional. Every finding shows the scanner that produced it.
Which one fits
Choose HostedScan if
- You want a lower bill. The pricing example below prices 25 targets on both.
- You need internal scanning without the top tier. It is on Premium at $109 per month billed annually.
- You run your own scanners and want their results in the same risk list.
- You need TLS and port scanning as separate scanners with their own reports.
Choose Intruder if
- You want scans to fire automatically when a new check is released.
- You want AWS, Azure, and GCP posture checks in the same product.
- You want more native integrations, including ServiceNow and Teams.
- You want a bigger G2 review footprint to support the purchase internally.
Capability matrix
Feature by feature
Differences come first. A half circle marks a limited capability, and its note names the limit. Notes about Intruder link to their source.
Feature


Scanners
Tenable Nessus
Nessus cloud scanning, Nessus scanners for internal networks, and Nessus Agents, all on Professional.
Pro tier only. Cloud tier scans with OpenVAS and Nuclei.
SourceDedicated TLS and certificate scanner
SSLyze certificate, protocol, and cipher checks on every plan.
SSL and TLS weaknesses are among the infrastructure checks, with no separate scanner or report.
SourceFull TCP and UDP port scanning
Full Nmap TCP and UDP port scans on every plan.
Exposed ports are part of the check set; full-range UDP is not a separate scan you configure.
SourceEmerging threat scans on new CVEs
The Greenbone feed updates daily and scans run on your schedule. No automatic rescan is triggered per new CVE.
Runs a check automatically as soon as one is released for a newly disclosed vulnerability.
SourceCoverage
Internal network scanning
An internal scanner runs inside your network on Premium. Nessus scanners and Nessus Agents on Professional.
SourceAgent-based internal scanning is a Pro feature.
SourceCloud configuration checks
No cloud configuration checks. Cloud accounts are connected only to import targets.
Cloud account connectors with posture checks, limited by tier.
SourceReporting and risk management
Import results from other scanners
Connect GitHub Dependabot and Snyk, and upload Nmap, OpenVAS, or ZAP results through the API.
SourceNo published import of third-party scanner results.
White-label reports
White-label PDF reports with your branding on Professional.
Watermarked reports on Free. No white-label option published.
SourceIntegrations and API
Licensing, pricing, and support
MSP and reseller program
MSP program with workspaces, white-label reports, and reseller pricing.
Reseller partner program. No multi-tenant workspace details published.
SourceHow the two products run
External scanning
Cloud scanners. Add a hostname, IP, URL, or CIDR and scan.
Cloud scanners. Add targets or connect a cloud account.
Internal scanning
An internal scanner inside your network on Premium. Nessus scanners and Nessus Agents on Professional.
A lightweight agent per host, on Pro and above.
Scanner upkeep
HostedScan maintains the scanners and syncs the Greenbone feed daily.
Intruder maintains the scanners and adds emerging-threat checks automatically.
Where data lives
HostedScan cloud, with PDF and HTML reports, CSV export from Premium, raw scanner output, and an API to pull everything.
Intruder cloud, with exports and an API.
What your team does weekly
Review new risks, accept or fix, export a report when the auditor asks.
Review new issues, triage, export a report.
Migration
How to switch from Intruder to HostedScan
The target list is the only thing you need to bring. Scan results are regenerated on the first run.
Carries over
- Targets and cloud connections
- Scan schedules
- Accepted-risk decisions, re-applied
- Compliance evidence, regenerated as PDF
Stays behind
- Historical scan results inside Intruder
- ServiceNow and Teams native integrations
- Emerging-threat automatic rescans
- 1
Export your targets
Download the target list from Intruder as CSV, or list them from your cloud accounts.
- 2
Import into HostedScan
Paste hostnames and IPs, upload the CSV, or connect AWS, Azure, or DigitalOcean and let discovery keep it current.
- 3
Run both in parallel
Scan the same targets during the 14-day trial and compare the finding lists side by side before you cancel anything.
- 4
Carry over accepted risks
Re-accept the known findings you had snoozed in Intruder so the first report is clean.
- 5
Move the integrations
Point Slack alerts, webhooks, and the Vanta connection at HostedScan. Rebuild any Jira automation on the API.
Pricing example
25 external targets, weekly scans, internal network scanning, and an API
One scenario priced on both products. HostedScan totals come from the published plan and per-target rates. Intruder figures were checked in September 2026 and link to the source.
HostedScan Premium
$1,908 / year
$159 per month billed annually. 5 targets included, 20 added at $2.50 each per month.
Premium includes authenticated ZAP scans, the internal scanner, REST API and webhooks, and every open-source scanner. Unlimited scans on all 25 targets.
Intruder
$6,190 / year
Pro, billed annually, for 25 infrastructure licenses. Pro is the tier with internal scanning. Cloud at 25 licenses is $3,910 per year without internal scanning.
From our customers
What our customers say

“As a SaaS company we are constantly at risk of cyberattacks, therefore an effective vulnerability scanner is a critical component of our information security toolkit. After an extensive search for an alternative solution, we found HostedScan and decided to give it a try. We are glad we did.”
Paolo Losi • CEO at Enuan

“We partnered with HostedScan to solve a critical need for our business: continuous, effective, and automated vulnerability scanning. We trust tools like OpenVAS, Zap and Nmap, but didn't have the time to automate them. HostedScan made it easy to scale them and organize the discovered vulnerabilities effectively.”
John Snyder • CEO

“HostedScan is a unified platform offering multiple scanning tools, and it's reasonably priced compared to leading scanners”
Quick Answers
Frequently asked questions
Our knowledge base contains answers to technical questions, and you can always contact us for more details on our plans, pricing, or any questions.
Speed and power,
without the complexity
The world's leading vulnerability scanners, all in one platform.